Latest Cybersecurity News and Articles
Low-Cost Android Phones Ship With Preinstalled Malware That Turns Them Into Residential Proxies
13 October 2026
Low-cost Android smartphones have been shipped with malicious software baked into the device firmware, allowing bad actors to covertly install apps, conduct ad fraud, and turn devices into residential proxies.
The activity, which targets Android devices built on MediaTek platforms across several brands, is being tracked by Bitdefender under the moniker Midnight Mimosa.
The preinstalled
⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More
12 October 2026
Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not much time to read the warning, let alone do something about it.
But speed is only part of the problem. A secure connection didn't always mean a safe destination. People offering to fix a ransomware mess had questions to answer themselves.
IonQ to Acquire Zero Trust Firm Elisity for Up to $1.3 Billion
12 October 2026
The all-stock deal brings Elisity’s least-privilege access technology into IonQ’s security portfolio.
The post IonQ to Acquire Zero Trust Firm Elisity for Up to $1.3 Billion appeared first on SecurityWeek.
Cyber-attack similar to OpenAI Medicare breach seems likely in UK, says minister
12 October 2026
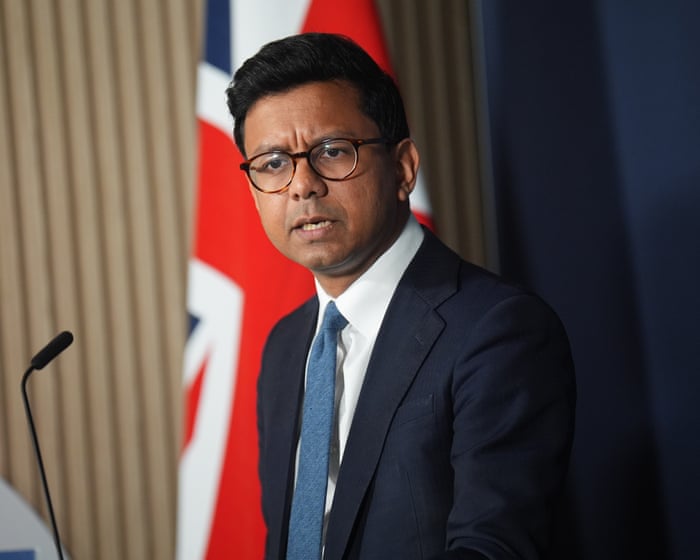 Kanishka Narayan, concerned by Australian incident, says British cyber defences could be bypassed by artificial intelligence agentUK politics live – latest updatesAn AI-driven cyber-attack similar to the OpenAI breach of Australia’s healthcare system is likely, “if not inevitable”, in the UK, according to a senior minister.Kanishka Narayan, the UK AI minister, indicated that the British government’s own cyber defences would be bypassed by a technology that has developed highly sophisticated skills in cybersecurity. Continue reading...
Bricksforge WordPress Plugin Vulnerability Exploited in the Wild
12 October 2026
The vulnerability tracked as CVE-2026-85097 can allow threat actors to take control of the targeted WordPress websites.
The post Bricksforge WordPress Plugin Vulnerability Exploited in the Wild appeared first on SecurityWeek.
Canonical Websites Disrupted in Second DDoS Attack This Year
12 October 2026
The outage hit the main Ubuntu and Canonical websites, including the Ubuntu blog and developer portal.
The post Canonical Websites Disrupted in Second DDoS Attack This Year appeared first on SecurityWeek.
Bring Your Own Agent: Your Employees' Assistants Are Already Logged In
12 October 2026
The personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta's Muse because it doesn't identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up.
Regardless, the tech world is mesmerized by the capabilities and potential of these services. Less than a year
Mastermind of 15,000-Mule Cybercrime Laundering Network Pleads Guilty in US
12 October 2026
Oleg Korniev was a leader of YMCO, a sophisticated network of money mules that helped hackers move funds outside the US.
The post Mastermind of 15,000-Mule Cybercrime Laundering Network Pleads Guilty in US appeared first on SecurityWeek.
Ledger Finds Unauthorized Hardware Implant in CryptoBilis-Sold Wallet Amid Fund Theft Reports
12 October 2026
Cryptocurrency hardware maker Ledger has temporarily paused sales of its products via CryptoBilis following reports of stolen funds linked to devices sold by the reseller.
On Friday, the company said it was investigating reports of loss of funds from users in Southeast Asia who had purchased products from CryptoBilis. The incident is said to have resulted in losses totaling more than $86
iRhythm Data Breach Impacts at Least 360,000 People
12 October 2026
Hackers stole patients’ personal information, including names, addresses, email addresses, dates of birth, and phone numbers.
The post iRhythm Data Breach Impacts at Least 360,000 People appeared first on SecurityWeek.
Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch
12 October 2026
Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure.
The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker "to direct the appliance to issue requests on their
Ransomware Response Expert Arrested in ShinyHunters FBI Hack Probe
12 October 2026
The suspect is believed to be Edward Dubrovsky, a Canadian cybersecurity executive who was visiting the United States for a conference.
The post Ransomware Response Expert Arrested in ShinyHunters FBI Hack Probe appeared first on SecurityWeek.
Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE
12 October 2026
A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack.
The critical vulnerability in question is CVE-2026-85097 (CVSS score: 10.0), which allows unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable WordPress websites, resulting in remote code execution (RCE). The
Critical SonicWall Vulnerability Exploited Days After Disclosure
12 October 2026
CVE-2026-102255 is a pre-authenticated SSRF flaw that could allow attackers to perform unauthorized operations.
The post Critical SonicWall Vulnerability Exploited Days After Disclosure appeared first on SecurityWeek.
Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch
12 October 2026
Beginning February 2027, all newly issued certificates will have a 64-day validity period by default.
The post Let’s Encrypt Cuts Default Certificate Validity to 64 Days Ahead of 45-Day Switch appeared first on SecurityWeek.
CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
12 October 2026
Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-commerce platforms, and critical infrastructure entities in Ukraine.
The activity, which brings together commodity offensive tools like Cobalt Strike with an AI orchestration layer powered by Anthropic's Claude Code, has been attributed
‘You have a meeting’: the calendar phishing scam growing exponentially
11 October 2026
 Appointment or renewal reminder appears in victims’ calendar to lure them into logging in to fake Google, Microsoft or PayPal pageYou’re preparing for the week ahead and take a look at your Google calendar. There’s an entry for a meeting that you must have completely forgotten. The note that pops up when you click on it says you’ll be reviewing a project and includes a link to more details. Confused, you follow it to find out more; the website you land on asks for logon details, and you provide them.Unfortunately, this was not a failure of your memory but a calendar phishing scam. You have handed your name and password to fraudsters who will sell it on in a batch with other people’s details, use it to break into your work email, or to persuade you that they are contacting you from your bank, or another institution. Continue reading...
The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn't
10 October 2026
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on. The other thousand are invisible to identity infrastructure by default, not because anyone hid them, but because an identity stack can only govern what authenticates through it, and most agents never do.
That gap is the clearest
Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison
10 October 2026
The former core infrastructure engineer deleted admin accounts, reset hundreds of passwords, and demanded 20 bitcoin to spare the company’s servers.
The post Insider Cyber Extortion Plot Against Industrial Firm Lands Engineer in Prison appeared first on SecurityWeek.
Anthropic Cuts Live Internet Access for Internal AI Tests After Claude Exploits Injection Flaws
10 October 2026
Anthropic on Friday said it's cutting off live internet access for all its internal evaluations following the discovery of new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior and targeted real websites.
The AI company said it identified four broad categories of unintended model actions during evaluations and internal use of Claude -
Claude Mythos