Latest Cybersecurity News and Articles
Anthropic Acquires Confidential AI Startup Opaque Systems
19 October 2026
Opaque Systems has developed technology that lets AI systems use sensitive data while keeping it protected by the underlying hardware.
The post Anthropic Acquires Confidential AI Startup Opaque Systems appeared first on SecurityWeek.
Unpatched Broadcom Wi-Fi Flaw Lets Attackers in Range Run Code as Root on Routers
19 October 2026
A flaw in Broadcom's Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or any pairing step, security researcher Quentin Kaiser disclosed on October 16.
He showed the attack working against home gateways supplied by three Belgian internet providers, in one case reading the Wi-Fi password off the device
OpenCode Console Breach May Have Exposed OpenAI, Anthropic, and Google API Keys
19 October 2026
An intruder reached a legacy system at OpenCode on the night of October 16 and may have exposed the third-party AI provider keys that users had saved in OpenCode Console, the company said.
Console is OpenCode's optional hosted service: a workspace saves its own OpenAI, Anthropic, or Google key there, and Console uses that key to call the provider so team members can use the models without
What are self-replicating ‘AI worms’, and why is Anthropic worried about them?
18 October 2026
 The tech company says successful AI worms need more capability on less powerful devices, but current trends make that feasible by the end of the yearWarnings about what artificial intelligence might do in the future – together with alarming reports of what it has gotten up to already – are being issued so quickly that even security experts have difficulty triaging what to worry about.Yet a report this week from Anthropic’s offensive research team grabbed attention by describing a new, practical threat, one devoid of human characteristics or apocalyptic musings. The red team, as such internal testers are called, said it created a malicious AI program that spread autonomously through internet-connected “smart” televisions and could do the same inside other ordinary devices. While machines running AI usually need a fair amount of computing power, the researchers said that their program split parts of itself among 15 televisions and was still able to function by using a bit of power from each. Continue reading...
US Cybersecurity Job Postings Fall 26% as AI Security Engineer Demand Soars
18 October 2026
CyberSN’s Cybersecurity Jobs Report provides visibility into the US cybersecurity job market. It’s a mixed bag.
The post US Cybersecurity Job Postings Fall 26% as AI Security Engineer Demand Soars appeared first on SecurityWeek.
ConnectWise Suspends Cloud Backup After Attackers Compromise Microsoft 365 Tenants
18 October 2026
ConnectWise on Saturday said it has disabled seven ConnectWise application identities as it continues its investigation into an incident in which unknown threat actors obtained unauthorized access to the application identities and compromised Microsoft 365 tenants.
The disabled identities are listed below -
ConnectWise Cloud Backup - 506e08f9-6e9a-4da4-942b-a099a03644ae
ConnectWise
Why Britain should reject the lure of cheap – and scary – Chinese AI
17 October 2026
 In the west the technology comes with at least some effort to provide security and a benign intent – not so from ChinaThere is much to fear from artificial intelligence developed in China and handed to businesses and governments in the west almost free of charge.Every month Chinese AI developers such as DeepSeek and Xiaomi dispatch the latest versions of their “open-weight” models that allow users to take the core software and use it without paying an expensive ongoing licence. Continue reading...
The power of AI is worrying senior Labour figures – as is the fear of ‘falling behind the public’
17 October 2026
 Westminster appears to be waking up to warnings over AI safety, with concerns over its use by extremist groups and bad actors“I have this sense that, within a few months, AI is going to be all anyone is talking about,” said one cabinet minister, with an ominous stare.It was Labour conference, with everyone from ministers to activists jubilant at Andy Burnham’s takeover and a bounce in the polls after the change of leader. Continue reading...
MALFEX npm Package 'imgdecode' Hides Shellcode Loader in Windows Native Addon
17 October 2026
Cybersecurity researchers have discovered a malicious npm package that's part of a recently disclosed software supply chain attack campaign dubbed MALFEX.
The package, named "imgdecode," was uploaded to the package registry on September 30, 2026, by a user named "malfexteste8." It has been downloaded 979 times as of writing and is still available on npm as of writing. The latest version of
Israeli Ad Firm Doubled as Candiru’s Zero-Click Spyware Delivery Channel
17 October 2026
Israeli company Discover-Tech’s ads allow threat actors to fingerprint and track devices at scale and infect selected targets.
The post Israeli Ad Firm Doubled as Candiru’s Zero-Click Spyware Delivery Channel appeared first on SecurityWeek.
Hackers Use Compromised ConnectWise Credential to Sign In to 173 Microsoft 365 Tenants
17 October 2026
Cybersecurity researchers are sounding the alarm related to an active campaign in which unknown threat actors are abusing a compromised Microsoft 365 (M365) credential belonging to ConnectWise Cloud Backup (formerly SkyKick) to gain unauthorized access to customers' M365 environments.
ConnectWise Cloud Backup is a cloud-based backup and recovery service built for managed service providers (MSPs
Not cool: who hacked France’s supermarket fridges?
17 October 2026
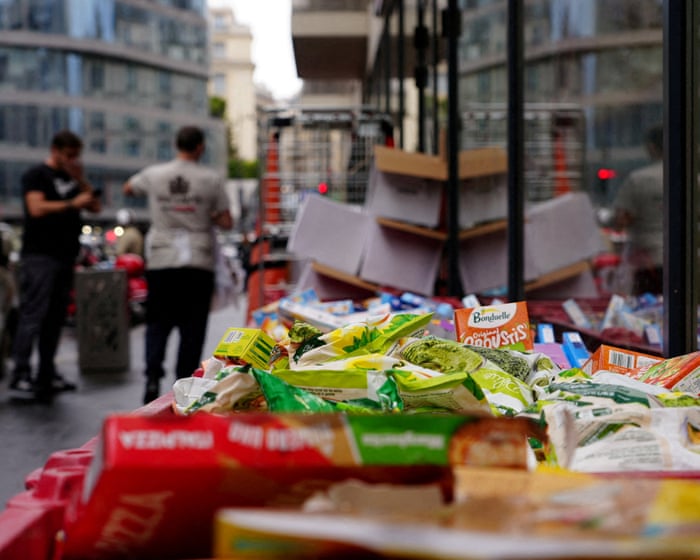 Whether it was youngsters proving their skills or state sabotage, Europe’s most hacked country was left with a mountain of waste after food began cooking in freezersShortly before midnight last Sunday, the digital thermostats controlling hundreds of supermarket cold aisles across France began to flicker and rise.In a “bizarre and unprecedented” cyber-attack, hackers had remotely overridden the temperature settings on thousands of freezers, fridges and chiller cabinets pushing them from as low as -27C (-16.6F) to well over 50C (122F). Continue reading...
Researchers Demonstrate OpenBSD Root Exploit Chaining 37-Year-Old Shared-Memory Bug
16 October 2026
A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing OpenBSD's KARL kernel-address randomization and its SMAP and SMEP hardware protections. Security firm Calif, which found and reported the flaws, published a detailed writeup and full proof-of-concept code after OpenBSD shipped
Attackers Tampered with AOMEI Backupper's Update Servers for Minutes to Deliver a Backdoor
16 October 2026
Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to ten minutes at a time between May and July 2026, so that any copy of the Windows backup program that checked for an update during one of those windows would download and run a backdoor.
Google Threat Intelligence Group, Mandiant, and ManageEngine's Threat Analysis
UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing
16 October 2026
Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct victims to an adversary-in-the-middle (AitM) phishing framework designed to harvest their Google account credentials and multi-factor authentication (MFA) codes.
The activity is being tracked by
In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit
16 October 2026
Noteworthy stories that might have slipped under the radar: BofA adds 1,000 patching contractors, KGB RAT pairs data theft with jump scares, and Langflow flaw under attack.
The post In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit appeared first on SecurityWeek.
OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract
16 October 2026
OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where its research model, after not having funds on an Ethereum test network, spent test cryptocurrency from a third-party's wallet without authorization to complete a coding task.
The incident, the AI company said, involved an internal research model part
BAE Systems Security Incident Stalls Notices From US Bankruptcy Courts
16 October 2026
A cyber incident affecting contractor BAE Systems has knocked out the Bankruptcy Noticing Center, halting notices nationwide for a week.
The post BAE Systems Security Incident Stalls Notices From US Bankruptcy Courts appeared first on SecurityWeek.
AI Decision Models and Their Impact on AI SOC Platforms
16 October 2026
In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive thinking. OpenAI announced its own Decisions API at DevDay and opened a public beta on October 6. Cribl published cribl-decision, an open LoRA adapter you can run locally. Others, like Laya, are
Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day
16 October 2026
Armory Castle exploited CVE-2026-102764 for initial access, deployed custom tools, and deleted logs and artifacts.
The post Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day appeared first on SecurityWeek.