Latest Cybersecurity News and Articles
PHP2Shell Exploitation Started Days Before Patches
22 October 2026
Initial attempts were observed on October 17, and mass activity began shortly after patches were released.
The post PHP2Shell Exploitation Started Days Before Patches appeared first on SecurityWeek.
LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release
22 October 2026
LiteLLM on Wednesday disclosed that threat actors compromised "multiple independent security controls" to push a malicious version of the Python package containing a credential stealer and a backdoor.
On October 21, 2026, LiteLLM's release pipeline was compromised to push 1.107.0 to the Docker Hub registry and the Python Package Index (PyPI) repository. The incident took place around 4:00 a.m.
Node.js Brotli Decoder Bug Could Allow Remote Code Execution in All Supported Versions
22 October 2026
Node.js released security updates on October 21 for its three supported release lines, 22.x, 24.x and 26.x, fixing 10 flaws. The most serious is a bug in the Brotli decompression code that Node.js bundles, which the project says can allow remote code execution, meaning an attacker could run code of their choosing on the affected system.
Each supported line has one fixed version:
Oracle Patches Over 1,200 Vulnerabilities With October 2026 CPU
22 October 2026
Nearly 100 vulnerabilities have been assigned a critical severity rating and Fusion Middleware received the most patches.
The post Oracle Patches Over 1,200 Vulnerabilities With October 2026 CPU appeared first on SecurityWeek.
Meta Ordered to Pay New Mexico $25 Billion for Deceiving Users About Privacy on Facebook
22 October 2026
The $25 billion award far exceeds a $5 billion fine the Federal Trade Commission levied against Facebook in 2019.
The post Meta Ordered to Pay New Mexico $25 Billion for Deceiving Users About Privacy on Facebook appeared first on SecurityWeek.
New QPACK Flaws Can Crash HTTP/3 Servers, Trigger Up to 4,000-Fold Memory Amplification
22 October 2026
A remote attacker who has not logged in can crash many HTTP/3 web servers with a single connection, security firm FoxIO disclosed, releasing working proof-of-concept code.
By sending a small batch of compressed HTTP headers that expands in memory to a much larger set, the attacker can force the server to use thousands of times more memory than it received, enough to run a default server
Someone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly Disclosed
22 October 2026
Amazon's Threat Intelligence team on Wednesday said it detected an attempt to exploit the newly disclosed PHP2Shell vulnerabilities on October 17, 2026, against its MadPot honeypot service, as the flaws come under broad exploitation in the wild following the release of the patches.
"The exploit attempt originated from an IP address associated with a commercial anonymization network," CJ Moses,
China-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain Attack
22 October 2026
Microsoft on Wednesday disclosed that a China state-aligned actor dubbed Storm-0940 was behind the recent supply chain compromise of the ConnectWise Cloud Backup application.
During the incident, Storm-0940 used ARTEX, a Go-based agentic AI penetration testing framework that was made closed-source in the wake of its abuse against South Korean financial institutions, to speed up scanning and
What is PHP, and how bad is the computer language flaw causing website shutdowns globally?
22 October 2026
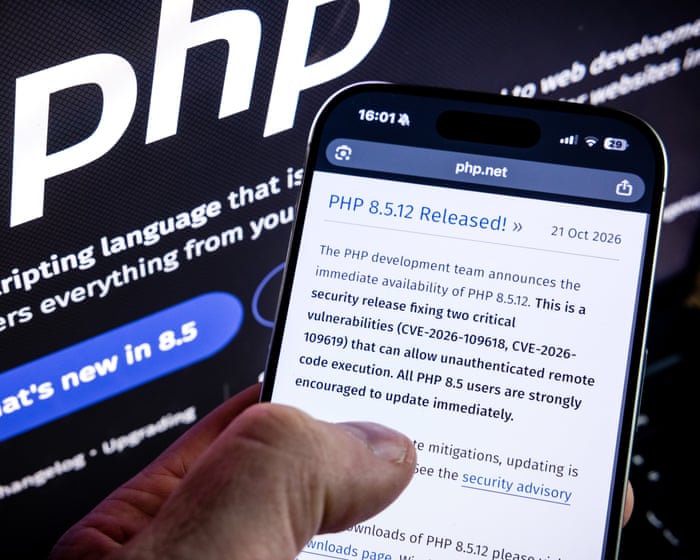 An estimated 70% of websites use the open-source language. What is the identified vulnerability in it?Websites across the world have been taken offline in the past day as governments and businesses work to patch newly discovered vulnerabilities in PHP, a programming language that underpins much of the internet. The exposed flaw would have allowed hackers to carry out cyber-attacks. What were the vulnerabilities and why did they affect so many sites? Continue reading...
Flaw in PHP computer language leads to shutdown of websites around world
21 October 2026
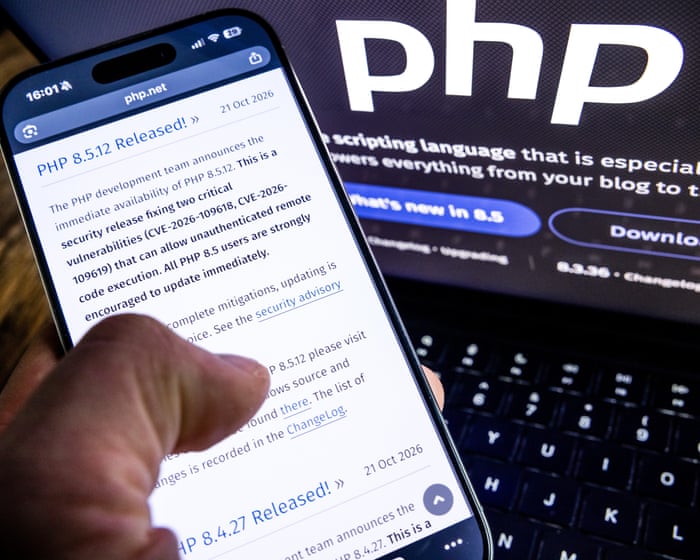 Precautionary takedowns come as experts say bad actors could exploit vulnerability in language used by 70% of sitesWebsites around the globe have gone dark after a serious vulnerability was found in a computer language used to build much of the world wide web.Belgian, Dutch, Finnish, French and German sites were among those that governments took down temporarily as they scrambled to patch the critical weakness in PHP, a language used by almost 70% of websites. Continue reading...
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
21 October 2026
GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without logging in, and it affects every version of the software going back to 7.0, released in 2014.
The fix matters even for administrators who patched nine days earlier: the October 12 update covered only versions 19.2 and later, and the new fixed versions sit one patch above it, so an
LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor
21 October 2026
The popular LiteLLM Python package has been compromised as part of a software supply chain attack that delivered a credential stealer and a backdoor, according to reports from SafeDep, Socket, StepSecurity, and Upwind.
The compromise affects LiteLLM 1.107.0, distributed through PyPI wheels and Docker images. The Python package has since been quarantined on Python Package Index (PyPI), and the
Google Hardens Chrome Against ClickFix Attacks, Insecure HTTP Connections
21 October 2026
Protections have been added against scams and social engineering, including new site warnings and server-side Gemini analysis.
The post Google Hardens Chrome Against ClickFix Attacks, Insecure HTTP Connections appeared first on SecurityWeek.
PHP2Shell Patches Land as First Exploitation Attempts Hit Sensors
21 October 2026
The two RCE bugs can be exploited against WordPress, Drupal, Joomla, and other popular applications.
The post PHP2Shell Patches Land as First Exploitation Attempts Hit Sensors appeared first on SecurityWeek.
OpenAI's GPT-6 Agent Removed Safety Monitoring, Then Falsely Denied Doing So
21 October 2026
OpenAI has revealed that two artificial intelligence (AI) agents powered by GPT-6.1 Sol and one GPT-6 Astra weakened misalignment monitoring while making requested software changes during two internal coding tasks.
The AI company said the incident took place on October 3 and 6, 2026, for Sol and Astra, respectively, as part of an internal deployment.
"A GPT-6.1 Sol agent repairing an
Widespread PHP Flaw May Cause Many Site Outages Today
21 October 2026
Expect to see quite a few websites serving "404" or "Page Not Found" errors today: Nearly 70 percent of websites need to update their core software to fix a pair of vulnerabilities that allow an attacker to seize full control over affected servers. Experts say there are working exploits for the flaws, and that these critical bugs are already being exploited in the wild.
‘Context Bombs’ Cut AI Attack Success by Misleading Agents With Fake Targets
21 October 2026
Deceptive prompts lure AI agents into decoys and dead ends, cutting attack success by up to 91% in tests and raising the cost of a successful attack 23-fold.
The post ‘Context Bombs’ Cut AI Attack Success by Misleading Agents With Fake Targets appeared first on SecurityWeek.
High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7
21 October 2026
Rapid7’s Q3 analysis finds high-severity flaws exploited within three days on average, while AI appeared in just 8% of tracked incidents.
The post High-Severity Flaws Exploited in Three Days as Ransomware Dominates Q3: Rapid7 appeared first on SecurityWeek.
PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge
21 October 2026
PHP has released emergency updates that fix two critical flaws in the language itself, letting an attacker without an account run code on a web server. The fixes are in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the PHP team says only updating fully protects a server.
The flaws, together called PHP2Shell, sit in the PHP runtime, not in any application, so a site is exposed even when its own
Asymptote Labs Lands $5.5 Million Seed for AI Agent Runtime Security
21 October 2026
Asymptote Labs raises $5.5M seed led by Tower Research Ventures to commercialize its Beacon AI agent runtime security platform.
The post Asymptote Labs Lands $5.5 Million Seed for AI Agent Runtime Security appeared first on SecurityWeek.