Latest Cybersecurity News and Articles
Nevada Ransomware: Another Feather in the RaaS Ecosystem
09 February 2023
A new ransomware family called Nevada Ransomware has emerged on underground forums. The actors behind this variant, as experts with Resecurity confirmed, have an affiliate platform first introduced in the RAMP underground community. The group recently distributed an updated locker—written in Rust— supporting encryption of Windows and Linux/ ESXi systems.
5 not-so-obvious predictions for the year ahead
09 February 2023
By Edwin Doyle, Global Cyber Security Evangelist. At the beginning of each year, CISOs, cyber vendors and other so-called experts are asked to make predictions about the upcoming year. What threats will we need to focus on and how can we stop them. It’s an understandable attempt at controlling the future; if only it were […]
The post 5 not-so-obvious predictions for the year ahead appeared first on CyberTalk.
Warning: Hackers Actively Exploiting Zero-Day in Fortra's GoAnywhere MFT
09 February 2023
A zero-day vulnerability affecting Fortra's GoAnywhere MFT managed file transfer application is being actively exploited in the wild.
Details of the flaw were first publicly shared by security reporter Brian Krebs on Mastodon. No public advisory has been published by Fortra.
The vulnerability is a case of remote code injection that requires access to the administrative console of the application
Massive ESXiArgs ransomware attack targets VMware ESXi servers worldwide
09 February 2023
Admins, hosting providers, and the French Computer Emergency Response Team (CERT-FR) warn that attackers actively target VMware ESXi servers unpatched against a two-year-old remote code execution vulnerability to deploy ransomware.
TruthFinder, Instant Checkmate confirm data breach affecting 20M customers
09 February 2023
PeopleConnect, the owners of the TruthFinder and Instant Checkmate background check services, confirmed they suffered a data breach after hackers leaked a 2019 backup database containing the info of millions of customers.
New Wave of Ransomware Attacks Exploiting VMware Bug to Target ESXi Servers
09 February 2023
VMware ESXi hypervisors are the target of a new wave of attacks designed to deploy ransomware on compromised systems.
"These attack campaigns appear to exploit CVE-2021-21974, for which a patch has been available since February 23, 2021," the Computer Emergency Response Team (CERT) of France said in an advisory on Friday.
VMware, in its own alert released at the time, described the issue as an
‘I’m not Snow White. I have to think like a criminal’: how I became a burglar for hire
09 February 2023
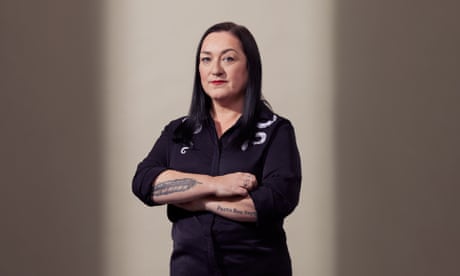 Jenny Radcliffe is a professional ‘people hacker’ – someone who claims she can get past anyone and get in anywhere. No building is secure. How does she do it? Plus, an extract from her memoir ‘Do I look like someone to mess with?” says Jenny Radcliffe, folding her arms in a really-don’t-mess-with-me kind of way. Her tattoos seem to be making the point, too. On her left forearm is a Latin phrase – facta non verba, actions not words – with a pair of devil’s horns; on her right, a feather, from the wings of an angel. Which is she, I wonder. Her boots – DM-like, many eyelets – suggest no angel; but the T-shirt is emblazoned with “Trust Me”.Radcliffe has an unusual job: she’s a social engineer. “Also known as a professional burglar, physical penetration tester … though it’s difficult to say that one to old ladies on trains,” she says. Yes, I can see that. Continue reading...
PixPirate: New Android Banking Trojan Targeting Brazilian Financial Institutions
09 February 2023
A new Android banking trojan has set its eyes on Brazilian financial institutions to commit fraud by leveraging the PIX payments platform.
Italian cybersecurity company Cleafy, which discovered the malware between the end of 2022 and the beginning of 2023, is tracking it under the name PixPirate.
"PixPirate belongs to the newest generation of Android banking trojan, as it can perform ATS (
Finland’s Most-Wanted Hacker Nabbed in France
09 February 2023
Julius "Zeekill" Kivimäki, a 25-year-old Finnish man charged with extorting a local online psychotherapy practice and leaking therapy notes for more than 22,000 patients online, was arrested this week in France. A notorious hacker convicted of perpetrating tens of thousands of cybercrimes, Kivimäki had been in hiding since October 2022, when he failed to show up in court and Finland issued an international warrant for his arrest.
What SOCs Need to Know About Water Dybbuk
09 February 2023
Once the email attachment is opened, the target’s computer will reach out to the command-and-control (C&C) server hosting a BadaxxBot toolkit that acts as a redirector to the final phishing page.
FormBook Malware Spreads via Malvertising Using MalVirt Loader to Evade Detection
09 February 2023
An ongoing malvertising campaign is being used to distribute virtualized .NET loaders that are designed to deploy the FormBook information-stealing malware.
"The loaders, dubbed MalVirt, use obfuscated virtualization for anti-analysis and evasion along with the Windows Process Explorer driver for terminating processes," SentinelOne researchers Aleksandar Milenkoski and Tom Hegel said in a
‘0ktapus’ hackers are back and targeting tech and gaming companies, says leaked report
09 February 2023
The hackers who reportedly hit more than 130 organizations last year and stole the credentials of almost 10,000 employees are still targeting several tech and video game companies, according to a report obtained by TechCrunch.
Mustang Panda APT Group Uses European Commission-Themed Lure to Deliver PlugX Malware
09 February 2023
The Mustang Panda APT group loads the PlugX malware in the memory of legitimate software by employing a four-stage infection chain that leverages malicious shortcut (LNK) files, triggering execution via DLL search-order-hijacking.
SaaS in the Real World: Who's Responsible to Secure this Data?
09 February 2023
When SaaS applications started growing in popularity, it was unclear who was responsible for securing the data. Today, most security and IT teams understand the shared responsibility model, in which the SaaS vendor is responsible for securing the application, while the organization is responsible for securing their data.
What’s far murkier, however, is where the data responsibility lies on the
OpenSSH Releases Patch for New Pre-Auth Double Free Vulnerability
09 February 2023
The maintainers of OpenSSH have released OpenSSH 9.2 to address a number of security bugs, including a memory safety vulnerability in the OpenSSH server (sshd).
Tracked as CVE-2023-25136, the shortcoming has been classified as a pre-authentication double free vulnerability that was introduced in version 9.1.
"This is not believed to be exploitable, and it occurs in the unprivileged pre-auth
Short-staffed SOCs struggle to gain visibility into cloud activities
09 February 2023
Enterprises have a limited number of analysts running their security operations centers (SOCs) and are deploying multiple tools in an attempt to address their cloud security challenges, according to ManageEngine.
InTheBox Sells Over 1,800 Android Phishing Forms
09 February 2023
Cyble observed the InTheBox threat actor selling over 1,800 web injects in its dark web shop, which can target users from Australia, Japan, Indonesia, the U.S., India, and other countries. The overlays support several Android banking trojans and impersonate apps operated by organizations across the globe. Due to the mass availability and low-cost web injects, threat actors are able to focus on other parts of their operations, including malware development and expansion of their attack surface.
Pupils across the UK crowned champions of the NCSC cyber contest for girls
09 February 2023
Thirteen teams around the country claimed victory at the finals of the 2023 CyberFirst Girls Competition
Russian Cybercriminals Launch New 'Passion' Attack Platform
09 February 2023
Medical institutions in the U.S. and Europe are under attack from a new botnet network called Passion launching DDoS attacks. It operates as a DDoS-as-a-Service (DDoSaaS) platform and has distinctive ties with Russian hacking groups, such as Anonymous Russia, Killnet, MIRAI, and Venom. It ran several defacement campaigns on Japanese and South African organizations in early January.
High-Severity Privilege Escalation Vulnerability Patched in VMware Workstation
09 February 2023
The flaw, tracked as CVE-2023-20854 and rated ‘high severity’, has been described by VMware as an arbitrary file deletion vulnerability affecting version 17.x on Windows.